HUMAN IDENTITY
ChainIT ID
ChainIT ID confirms the human signer through biometric verification tied to authoritative sources: not just an email address or password.

Scan the QR Code with your phone to download the app.

A signed vendor agreement means nothing if the signer never had the authority to bind their company. ChainIT gives procurement teams a full verification stack (identity, organization, authority, and rules) checked automatically before any contract executes, and sealed into immutable proof the moment it does.
Procurement risk rarely comes from a forged signature. It comes from a signature that's completely real: attached to someone who was never authorized to make that specific commitment.
ChainIT closes that gap with a connected stack of products, each solving one piece of the verification chain:
ChainIT ID confirms the human signer through biometric verification tied to authoritative sources: not just an email address or password.
ChainIT Organization ID confirms the vendor is a real, active entity, checked against authoritative registries rather than a self-submitted document that may already be outdated.
Authority Resolution Pactvera (ARP) determines whether this specific signer actually has the authority to bind their organization: and within what scope, value limit, and timeframe.
Business Rules Engine (BRE) evaluates whether the proposed transaction falls within that signer's authorized domain, blocking execution automatically if it doesn't.
Pactvera governs the agreement itself, allowing it to proceed only once identity, organization, and authority all align.
Business Process Orchestration (BPO) ensures every required step — verification, authority confirmation, evidence capture: happens in the correct order, not just eventually.
Tokenized Consideration Asset (TCA) ties payment release directly to the agreement, so funds only move once contract conditions are verifiably met.
Valitorum seals the final proof (person, organization, authority, rules, and execution context) into one immutable record.
No single product carries the full weight. Together, they replace "the signer looked legitimate" with a provable chain procurement teams can actually stand behind.
Because procurement risk doesn't live in one place: it hides in the gaps between systems.
E-signature platforms confirm someone clicked. They can't tell you whether that person was allowed to commit their organization to this specific deal. ARP and BRE exist precisely to close that gap.
Verifying a vendor once at onboarding doesn't mean their signing authority is still valid six months later. ChainIT Organization ID and ARP work together to confirm current, not historical, authority.
When a contract lives in one system and payment moves through another, nothing confirms the money only released because conditions were actually met. TCA closes that by binding value exchange directly into the agreement.
Under deadline pressure, teams skip steps: verify later, get approval after the fact. BPO makes the correct order structurally required, not just procedurally suggested.
Without Valitorum, resolving a disputed vendor agreement means reconstructing events from emails, spreadsheets, and memory. With it, the answer already exists.
Each product plugs a specific hole. Together, they remove the seams where procurement risk usually gets in.
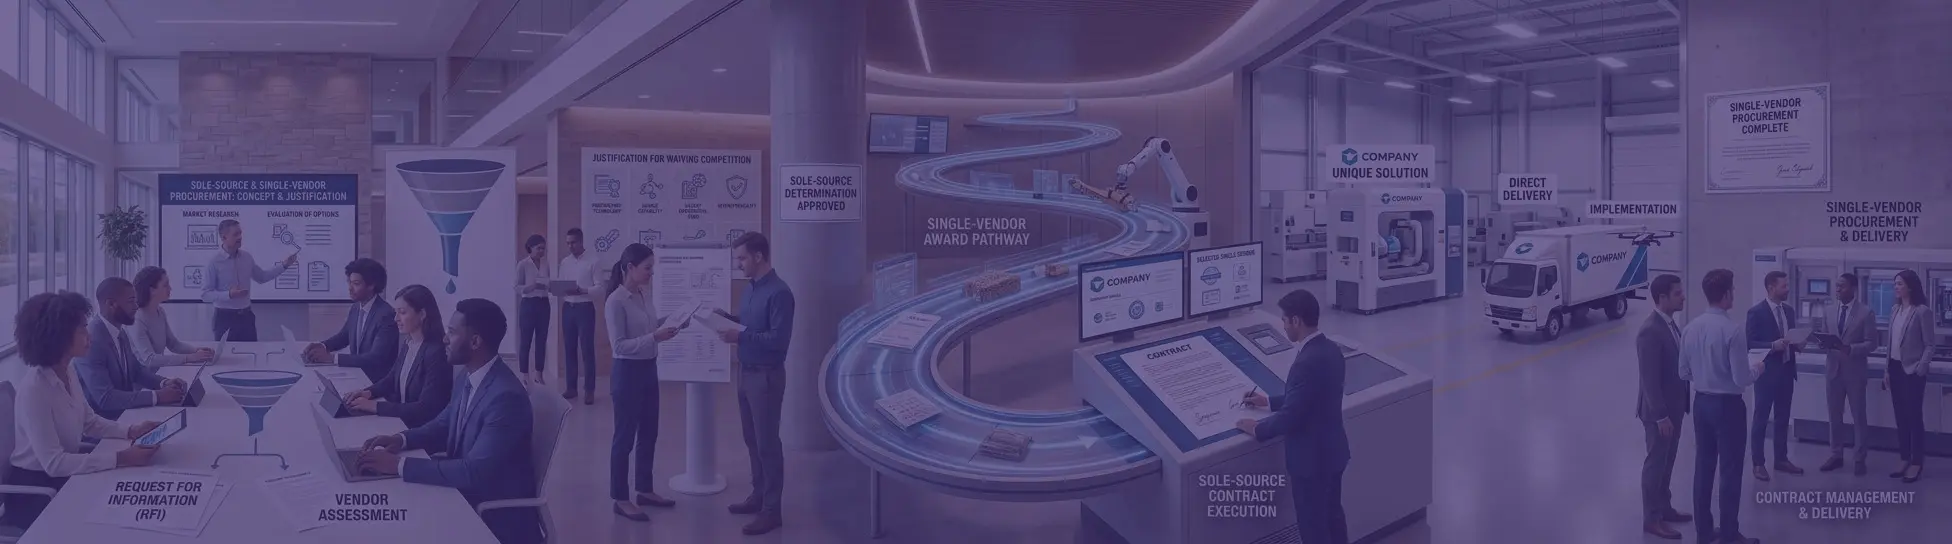
Whatever category your procurement falls into, the same standard applies: verified person, verified organization, verified authority and every time.
Verify a new supplier's organizational standing and the signer's authority before the relationship even begins, not after a contract is already in dispute.
Confirm that purchase agreements, service contracts, and recurring supply commitments are executed by someone actually authorized for that category and value range.
Apply stronger authority and Token Grade thresholds automatically to large or strategic commitments, where the cost of an authority failure is highest.
Ensure ongoing authority remains valid across the life of a multi-year or renewing contract, catching revoked or expired delegation before renewal executes.
Add extra scrutiny where competitive bidding doesn't provide a natural check: verifying vendor legitimacy and signer authority carries more weight here, not less.
Apply jurisdiction-aware authority and compliance rules automatically, so international vendor agreements meet the right regulatory bar for each region involved.
Keep authority and rule checks intact even under time pressure, so "we needed it fast" never becomes an excuse for skipping verification.
Give autonomous procurement agents a verified authority chain to check before committing the organization, so automation never outruns governance.
Whatever category your procurement falls into, the same standard applies: verified person, verified organization, verified authority and every time.
ChainIT provides cryptographically verifiable state for identities, organizations, assets, devices, and authority. Every workflow, enterprise application, and AI agent can consume authoritative proof before executing decisions, approvals, settlements, or autonomous actions.
